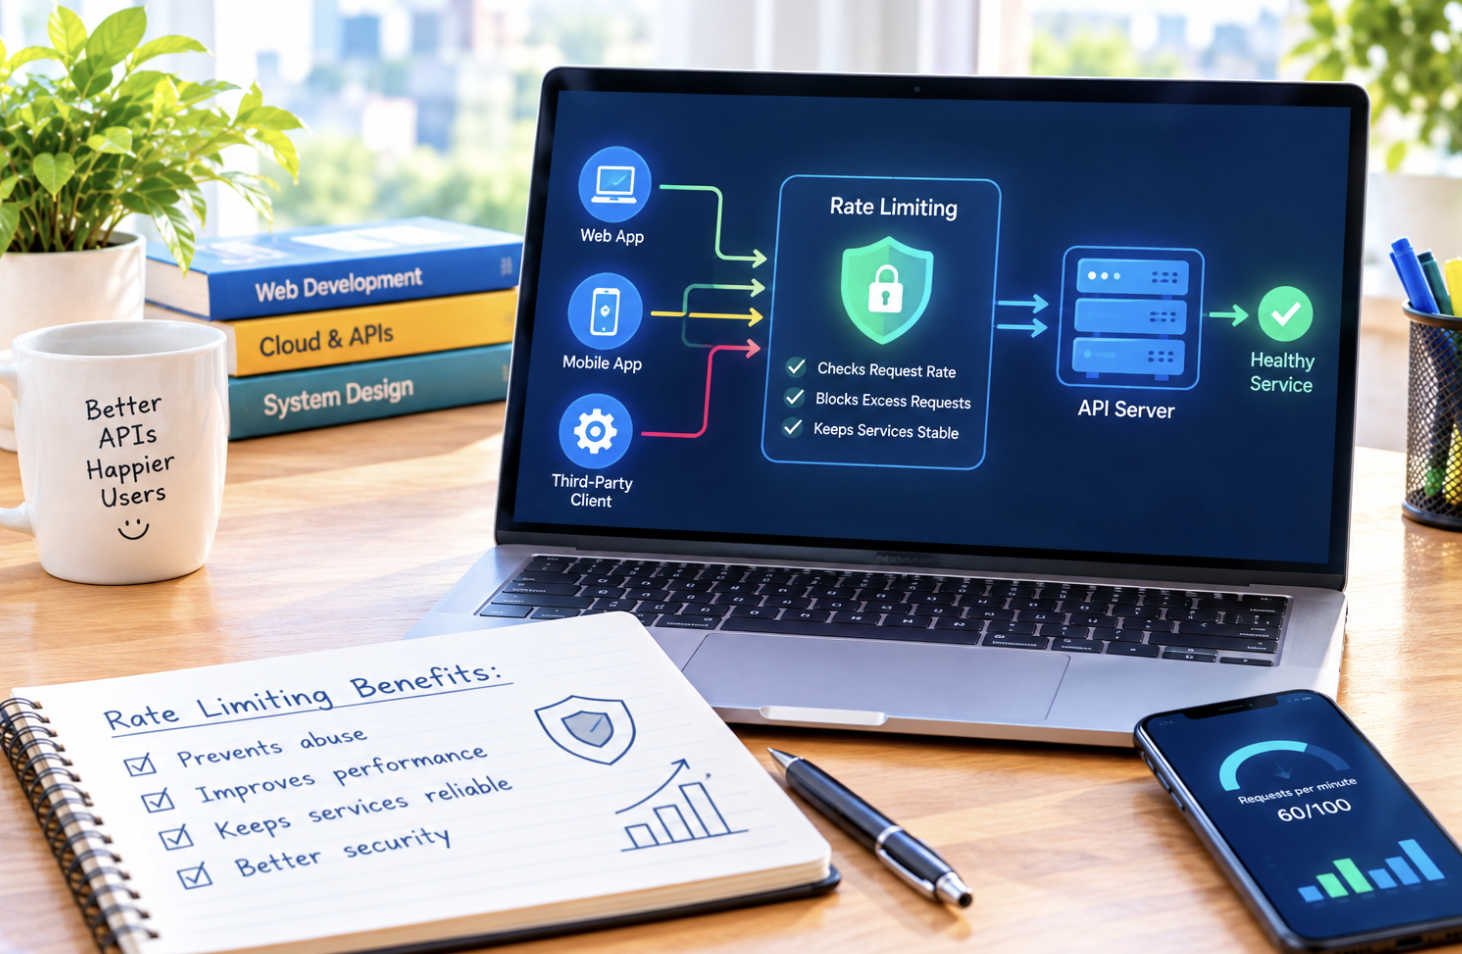
A small startup’s API went from handling a comfortable few hundred requests per minute to being completely overwhelmed within an hour, not because of a sudden surge in legitimate customers, but because a single misconfigured script from one client kept retrying failed requests in a tight, endless loop. The entire service ground to a halt for every customer, not just the one causing the problem. A single rate limiting rule, added after the incident, would have contained the damage to that one client’s requests instead of taking down the whole platform.
What API Rate Limiting Does
Rate limiting is a technique that restricts how many requests a client, whether a user, an application, or an automated script, can make to an API within a specified time window. Once a client exceeds the defined limit, the API typically responds with an error indicating the limit has been reached, rather than processing the excess requests, protecting the underlying service from being overwhelmed by any single source, whether that source is malicious, misconfigured, or simply more active than the system was designed to handle.
Why Every Production API Needs Rate Limiting
Without rate limiting, an API has no built-in defense against a wide range of scenarios that can degrade or completely disrupt service for every user, not just the one causing the problem.
- Malicious actors attempting denial-of-service attacks by flooding an API with excessive requests
- Poorly written client code that retries failed requests in rapid, uncontrolled loops
- Legitimate but unexpectedly heavy usage from a single client that consumes disproportionate server resources
- Automated scraping or data harvesting that can degrade performance for users if left unrestricted
Rate limiting doesn’t just protect against bad actors, a significant portion of real-world incidents trace back to legitimate clients with buggy retry logic or unexpectedly heavy usage patterns, making rate limiting a defense against accidents as much as against deliberate abuse.
Common Rate Limiting Algorithms Explained
Several distinct algorithmic approaches exist for implementing rate limiting, each with different trade-offs around accuracy, memory efficiency, and how they handle traffic bursts.
- Fixed window counting tracks requests within discrete time blocks, such as per minute, resetting the count at each new window
- Sliding window approaches track requests within a continuously moving time frame, providing smoother, more accurate limiting than fixed windows
- Token bucket algorithms allow controlled bursts of traffic while maintaining a steady average rate over time
- Leaky bucket algorithms process requests at a constant, steady rate regardless of how bursty the incoming traffic pattern is
The choice between these algorithms depends on the specific API’s traffic patterns and tolerance for burstiness. A payment processing API might prioritize the steady, predictable processing of a leaky bucket approach, while a content API serving occasional traffic spikes might prefer a token bucket’s flexibility to accommodate legitimate bursts.
Setting Rate Limits at the Right Level
Effective rate limiting often applies different limits at different levels, rather than a single blanket rule applied uniformly across every type of request and user.
- Per-user or per-API-key limits, tracking usage individually for each authenticated client
- Per-IP-address limits, useful for controlling unauthenticated or public-facing endpoint abuse
- Per-endpoint limits, recognizing that some API endpoints are more resource-intensive than others and deserve stricter limits
- Global service-wide limits, providing a final backstop against total system overload regardless of how traffic is distributed
Layering these different levels together provides more nuanced protection than a single rule ever could, allowing a service to remain generous with well-behaved, authenticated clients while remaining strict against unauthenticated or suspicious traffic patterns.
How Rate Limits Get Communicated to API Clients
Well-designed APIs don’t just enforce rate limits silently, they communicate limit status clearly, allowing well-behaved client applications to adjust their behavior proactively rather than repeatedly hitting a limit and receiving errors.
- Response headers indicating the current rate limit, how many requests remain, and when the limit resets
- Clear, specific error messages when a limit is exceeded, rather than a generic, unhelpful failure response
- Retry-after guidance telling clients exactly how long to wait before making another request
- Documentation clearly explaining rate limit tiers and how they vary across different account types or subscription levels
This transparency matters for developer experience. An API that fails silently or with unclear error messages when rate limited creates unnecessary frustration and support burden compared to one that clearly communicates limits and guides clients toward appropriate, compliant behavior.
Different Rate Limiting Tiers for Different User Types
Many APIs implement tiered rate limiting, offering different limits based on account type, subscription level, or trust status, rather than applying identical limits to every client regardless of their relationship with the service.
- Free tier accounts typically receive more restrictive rate limits than paid subscription tiers
- Enterprise or high-volume customers often negotiate custom, higher rate limits suited to their specific usage needs
- Newly registered or unverified accounts sometimes receive stricter initial limits until an account establishes a track record
- Internal or trusted partner integrations may operate under separate, more permissive rate limiting rules entirely
This tiered approach allows a service to balance protecting infrastructure with providing a usable experience for legitimate high-volume customers, rather than applying a one-size-fits-all limit that either under-protects the system or unnecessarily restricts paying customers with legitimate heavy usage needs.
The Trade-off Between Protection and User Experience
Rate limiting inherently involves a balancing act, since overly aggressive limits frustrate legitimate users while overly permissive limits fail to adequately protect the underlying service.
- Setting limits too conservatively frustrates legitimate users and can drive them toward competing services
- Setting limits too permissively fails to prevent the exact abuse scenarios rate limiting is meant to guard against
- Monitoring actual usage patterns over time helps calibrate limits based on real data rather than initial guesses
- Providing clear paths for legitimate users to request higher limits reduces frustration from overly conservative defaults
Getting this balance right typically requires iteration based on real usage data rather than assuming initial limits set before launch will remain appropriate indefinitely as actual usage patterns and user needs become clearer over time.
Monitoring and Alerting for Rate Limit Violations
Beyond simply enforcing limits, effective rate limiting systems include monitoring and alerting that help operations teams understand traffic patterns and respond proactively to unusual activity before it becomes a larger problem.
- Dashboards tracking rate limit violations by client, endpoint, and time period reveal patterns worth investigating further
- Automated alerts for unusual spikes in rate limit violations can flag potential attacks or misconfigured clients quickly
- Historical trend analysis helps distinguish between a one-time traffic spike and a sustained, escalating pattern of abuse
- Correlating rate limit data with other security signals provides a more complete picture than rate limiting data viewed in isolation
Teams that treat rate limiting purely as a passive enforcement mechanism, without building monitoring on top of it, miss valuable early warning signals that the underlying data already contains about both technical problems and potential security concerns worth investigating.
Rate Limiting in Distributed, Multi-Server Environments
Implementing rate limiting correctly becomes more complex once an API runs across multiple servers rather than a single machine, since tracking request counts accurately requires coordination between all the servers handling traffic.
- Distributed rate limiting requires a shared, centralized counter accessible to all servers handling API requests
- In-memory rate limiting on a single server doesn’t work correctly once traffic is load-balanced across multiple servers
- Centralized, fast data stores are commonly used to maintain accurate, shared rate limit counters across a distributed system
- Network latency to this shared counter can introduce its own performance considerations that need to be carefully managed
Getting distributed rate limiting right is a nontrivial engineering challenge, and many early-stage rate limiting implementations that work correctly in testing on a single server reveal subtle bugs only once traffic scales across multiple production servers running simultaneously.
Handling Authentication Failures Gracefully Alongside Rate Limits
Rate limiting and authentication failures often interact in ways that require careful design, since attackers frequently probe both systems together, and poorly coordinated handling of the two can create security gaps or usability problems.
- Failed authentication attempts should typically count toward rate limits to prevent brute-force credential guessing attacks
- Rate limits on authentication endpoints often need to be stricter than limits on general API endpoints
- Clear separation between “rate limited” and “authentication failed” error messages helps legitimate users troubleshoot without revealing too much to attackers
- Temporary account lockouts after repeated failures serve a related but distinct security purpose from general rate limiting
Designing these two systems to work together coherently, rather than treating rate limiting and authentication security as entirely separate concerns, closes gaps that attackers have historically exploited by working just below the threshold of either system individually.
Testing Rate Limiting Configuration Before Production Deployment
Properly testing rate limiting logic before deploying it to a live, production API prevents both the embarrassment of overly aggressive limits blocking legitimate users and the risk of limits too permissive to provide meaningful protection.
- Load testing tools can simulate realistic traffic patterns to verify rate limiting behaves as expected under real conditions
- Testing edge cases, like requests arriving exactly at a rate limit window boundary, catches subtle implementation bugs
- Staged rollouts, starting with more permissive limits and tightening gradually based on observed data, reduce the risk of disrupting real users
- Documenting expected rate limiting behavior clearly helps both internal teams and external API consumers understand what to expect
Skipping thorough testing before deploying rate limiting changes is a common way well-intentioned protective measures end up causing more disruption than the abuse scenarios they were originally designed to prevent in the first place.
How API Versioning Interacts With Rate Limiting Policy
API versioning and rate limiting policy often need to be coordinated carefully, when an organization maintains multiple active API versions simultaneously for different groups of clients.
- Different API versions sometimes warrant different rate limiting policies based on their relative efficiency or resource demands
- Deprecated API versions might intentionally receive stricter rate limits to encourage migration toward newer, more efficient versions
- Clear communication about version-specific rate limiting differences helps developers plan migrations appropriately
- Maintaining consistent rate limiting documentation across all actively supported API versions reduces developer confusion and support requests
Organizations that overlook this coordination sometimes create confusing situations where seemingly identical requests behave differently depending on which API version a client happens to be using, a source of confusion that clear, version-specific documentation can prevent.
How Third-Party API Gateways Simplify Rate Limiting Implementation
Rather than building rate limiting logic entirely from scratch, many organizations rely on dedicated API gateway tools that handle this functionality alongside other cross-cutting API concerns.
- API gateways centralize rate limiting, authentication, and traffic routing in a single, dedicated infrastructure layer
- This centralization avoids duplicating rate limiting logic separately across many individual backend services
- Gateway-based rate limiting typically includes built-in support for the tiered and multi-level limiting strategies discussed earlier
- Adopting a gateway does introduce an additional infrastructure component that itself needs proper configuration and monitoring
For organizations running many microservices, a dedicated gateway often proves more maintainable long-term than implementing and maintaining separate rate limiting logic independently within each individual backend service across a growing system.
Considering Fairness Across Different Client Sizes
Rate limiting policy inevitably raises fairness questions when clients of very different sizes share the same infrastructure, since a limit generous enough for a large enterprise client might be excessive for protecting the system from a much smaller client’s misbehavior, while a limit appropriately strict for smaller clients might unnecessarily constrain legitimate large-scale usage.
Thoughtful tiering, informed by actual observed usage data rather than assumptions made before launch, tends to produce a fairer and more sustainable outcome than a single uniform limit applied indiscriminately across an entire diverse client base.
Final Thoughts
API rate limiting is one of those infrastructure decisions that’s easy to overlook until the exact moment it becomes critically necessary, usually during an incident that a properly configured limit would have prevented entirely. Building it in deliberately from the start, with clear communication to clients and thoughtful tiering based on actual usage patterns, protects both the service’s stability and the experience of every legitimate user depending on it.
Frequently Asked Questions
What happens when a client exceeds an API’s rate limit?
Typically, the API returns a specific error response, commonly using an HTTP status code indicating too many requests, along with information about when the client can try again. Well-designed APIs include this retry guidance directly in the error response rather than leaving clients to guess when it’s safe to retry.
Can rate limiting fully prevent denial-of-service attacks?
Rate limiting is one important layer of defense but generally isn’t sufficient on its own against sophisticated, distributed denial-of-service attacks, which often use many different sources to circumvent per-client limits. Comprehensive protection typically combines rate limiting with additional defenses like traffic filtering and dedicated anti-DDoS infrastructure.
How do APIs handle legitimate traffic spikes without over-restricting users?
Token bucket and similar burst-tolerant algorithms are specifically designed to accommodate legitimate short-term traffic spikes while still maintaining an overall average rate limit, allowing well-behaved clients some flexibility rather than strictly capping every short burst of otherwise normal usage.
Do all APIs use the same rate limiting approach?
No, rate limiting implementation varies across different APIs and services, depending on their specific traffic patterns, infrastructure, and business requirements. There’s no single universal standard, though certain algorithms and communication patterns, like standard rate limit response headers, have become common conventions across the industry.
How can developers avoid hitting rate limits unexpectedly?
Reading API documentation carefully to understand specific limits, implementing proper error handling and retry logic with appropriate backoff delays, and monitoring rate limit response headers proactively all help developers build applications that respect limits gracefully rather than triggering them unexpectedly.
Is rate limiting only relevant for large-scale APIs?
No, even small applications benefit from rate limiting, since a single misconfigured client, whether malicious or simply buggy, can overwhelm even a modestly sized service if there are no restrictions in place, exactly the kind of incident that led to prioritizing rate limiting as a standard practice at services of all sizes.